WordPress powers millions of websites worldwide, making it one of the most popular website platforms on the internet. But popularity also attracts attention from hackers, bots, malware distributors, and automated attacks. Whether you run a business website, blog, online store, or portfolio, protecting your WordPress files is one of the most important parts of keeping your website safe.
Many website owners focus only on design and content while ignoring file security. Unfortunately, vulnerable WordPress files can expose your database, themes, plugins, login information, and even customer data. A single weak file permission or outdated plugin can become an entry point for attackers.
The good news is that WordPress file protection does not always require advanced coding skills. With the right security practices, you can significantly reduce the risk of unauthorized access, malware infections, and file manipulation.
In this guide, you will learn how to protect WordPress files using practical and beginner-friendly methods. From securing wp-config.php to managing file permissions and blocking malicious access, these strategies can help keep your website safer and more stable.
Why WordPress File Protection Matters
Every WordPress website contains critical system files that control how the site operates. Some files handle database connections, while others manage plugins, themes, uploads, and user authentication.
If attackers gain access to these files, they may:
- Inject malware
- Redirect visitors to spam websites
- Steal login credentials
- Delete website content
- Modify plugin or theme files
- Install hidden backdoors
- Access customer information
Many website compromises happen because of simple security mistakes. Weak passwords, outdated plugins, incorrect permissions, and unsecured hosting environments are common causes.
Learning how to protect WordPress files helps reduce these risks and improves overall website stability.
Maintenez WordPress à jour
One of the simplest ways to protect WordPress files is by keeping everything updated.
Cela comprend :
- Noyau WordPress
- Thèmes
- Plugins
- PHP version
Updates often include security patches that fix known vulnerabilities. Hackers actively scan websites running outdated software because those weaknesses are publicly documented.
Why Updates Matter
When developers discover security flaws, they release updates to fix them. If your website stays outdated, attackers may exploit those vulnerabilities before you even notice.
Enable automatic updates whenever possible for:
- Minor WordPress core updates
- Trusted plugins
- Trusted themes
Before major updates, always create a backup to avoid compatibility problems.
Use Strong File Permissions
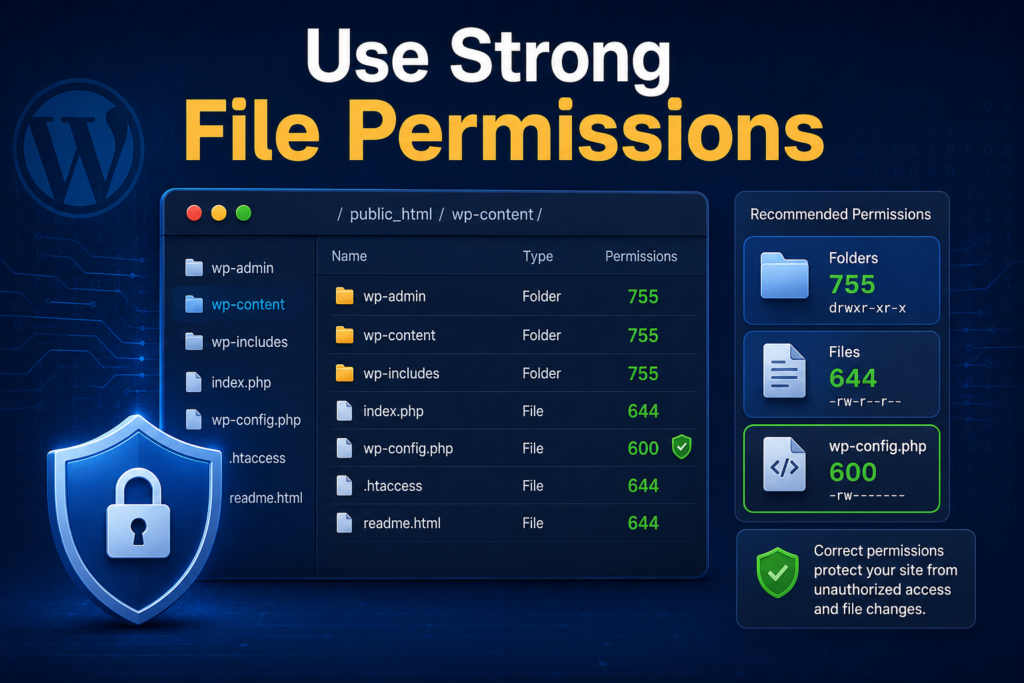
File permissions determine who can read, write, or execute files on your server.
Incorrect permissions are one of the biggest WordPress security mistakes.
Recommended WordPress File Permissions
Typical secure settings include:
| File Type | Recommended Permission |
|---|---|
| Files | 644 |
| Folders | 755 |
| wp-config.php | 600 or 640 |
These settings help prevent unauthorized users from modifying important files.
Why Permissions Matter
If permissions are too open, attackers may upload malicious scripts or modify existing files.
Par exemple:
777permissions are extremely risky- Public write access can expose your entire website
- Shared hosting environments become more vulnerable with weak permissions
Most hosting panels allow permission changes through:
- File Manager
- FTP clients
- SSH access
Always verify permissions after migrations or plugin installations.
Protect the wp-config.php File
Le wp-config.php file is one of the most sensitive files in WordPress.
It contains:
- Database credentials
- Authentication keys
- Security configurations
- Table prefixes
If attackers access this file, they may gain control over your entire website.
How to Secure wp-config.php
Several common protection methods include:
- Restricting file permissions
- Blocking public access
- Moving the file outside the public root directory
- Disabling file viewing through server rules
Many website owners also use server-level configurations to deny external access to this file.
Protecting wp-config.php should always be a top priority when learning how to protect WordPress files.
Disable File Editing in the Dashboard
By default, WordPress allows administrators to edit plugin and theme files directly inside the dashboard.
While convenient, this feature can become dangerous if an attacker gains admin access.
Why Disable File Editing
Hackers often inject malicious code into:
- fichiers de thème
- Plugin files
- Header scripts
- Footer scripts
Disabling file editing helps reduce this risk.
Many security-conscious website owners turn this feature off entirely, especially on production websites.
Use Secure Hosting
Your hosting provider plays a major role in website security.
Even if your WordPress settings are perfect, weak hosting infrastructure can still expose your files.
Features of Secure WordPress Hosting
Look for hosting providers that offer:
- Malware scanning
- Firewalls
- Daily backups
- Isolated accounts
- DDoS protection
- Automatic updates
- Web application firewalls
- Server-side caching
- Security monitoring
Cheap hosting plans sometimes sacrifice security for lower costs.
Reliable hosting can significantly improve WordPress file protection.
Install a WordPress Security Plugin
Security plugins can help monitor, scan, and protect your WordPress files.
Popular features often include:
- Malware detection
- Login protection
- File integrity monitoring
- Firewall protection
- Brute-force prevention
- Security alerts
- Bot blocking
What File Monitoring Does
Some plugins compare your current files with original WordPress core files.
If suspicious changes appear, the plugin alerts you immediately.
This helps detect:
- Malware injections
- Unauthorized modifications
- Hidden backdoors
- Corrupted files
File monitoring is especially useful for business websites and online stores.
Limiter les tentatives de connexion
Brute-force attacks are extremely common on WordPress websites.
Attackers use automated bots to repeatedly guess usernames and passwords.
How Login Protection Helps
Limiting login attempts can:
- Block repeated failed logins
- Slow down attack bots
- Reduce server abuse
- Protect admin accounts
Combining login limits with strong passwords and two-factor authentication creates a much safer environment.
Activer l'authentification à deux facteurs
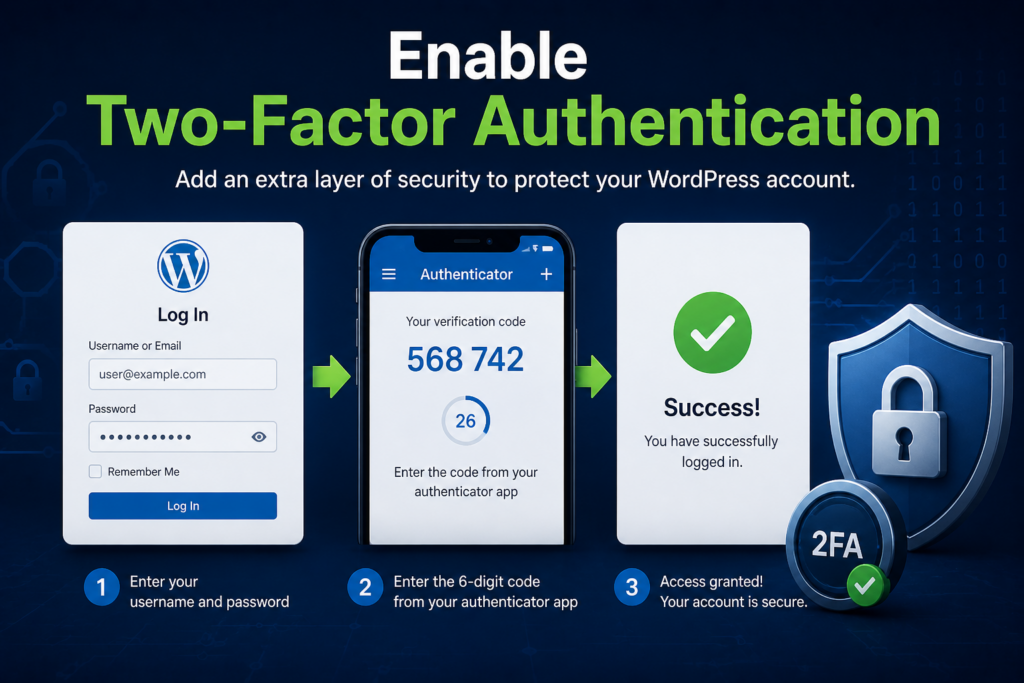
Two-factor authentication adds an extra layer of security.
Instead of relying only on passwords, users must also verify their identity through another method.
Exemples :
- Authentication apps
- Email codes
- Mobile verification
Even if hackers steal your password, they may still fail to access your dashboard without the second verification step.
This is one of the most effective ways to secure WordPress admin access.
Use Strong Passwords
Weak passwords remain one of the biggest causes of hacked websites.
Avoid passwords like:
- admin123
- password
- qwerty
- 123456
Better Password Practices
Use passwords that contain:
- Uppercase letters
- Lowercase letters
- Numbers
- Special characters
Longer passwords are generally harder to crack.
Password managers can also help generate and store secure credentials safely.
Rename the Default Admin Username
Many automated attacks target the default username:
admin
Changing the administrator username makes brute-force attacks more difficult.
Pourquoi c'est important
Hackers already know many websites use predictable usernames.
When the username is hidden or unique, attackers must guess both:
- Username
- Password
This creates an additional security barrier.
Backup Your Website Regularly
Backups are essential for WordPress security.
Even secure websites can still experience:
- Infections par logiciels malveillants
- Human mistakes
- Plugin conflicts
- Hosting failures
- Data corruption
What a Good Backup Includes
A complete backup should contain:
- Database files
- Thèmes
- Plugins
- Uploads
- WordPress core files
Store backups in multiple locations, such as:
- Cloud storage
- External drives
- Remote servers
Automatic backups provide additional protection against unexpected issues.
Protect the Uploads Folder
The uploads directory stores media files such as:
- Images
- PDFs
- Videos
- Downloads
Attackers sometimes upload malicious scripts disguised as media files.
How to Secure Uploads
Website owners often:
- Restrict executable file types
- Block PHP execution inside uploads
- Scan uploaded files
- Limit upload permissions
This helps prevent attackers from running harmful scripts through the media folder.
Use SSL Certificates
SSL certificates encrypt data between visitors and your website.
Websites using HTTPS are generally safer than those using plain HTTP.
Benefits of SSL
SSL helps protect:
- Login credentials
- Payment information
- soumissions de formulaires
- User sessions
Search engines also prefer secure HTTPS websites.
Most hosting providers now offer free SSL certificates through services like Let’s Encrypt.
Remove Unused Plugins and Themes
Unused plugins and themes still create security risks.
Even inactive software can contain vulnerabilities.
Why Cleanup Matters
Old plugins may:
- Stop receiving updates
- Become incompatible
- Introduce hidden vulnerabilities
Delete anything you no longer use.
Keeping your WordPress installation lean improves both:
- Sécurité
- Performance
Hide Your WordPress Version
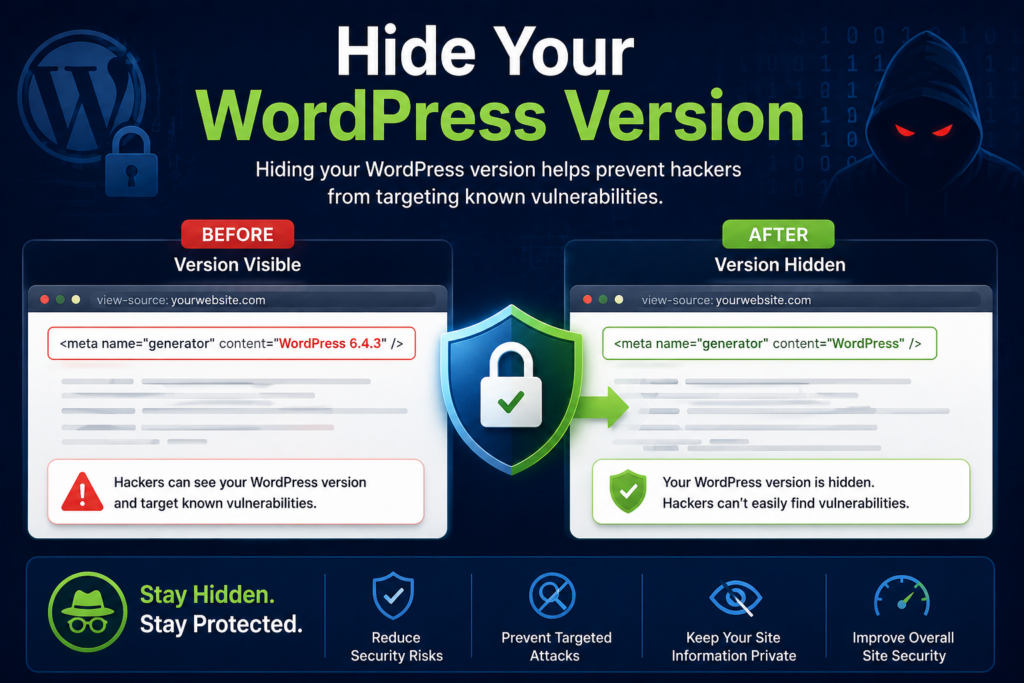
Displaying your WordPress version publicly may help attackers identify vulnerabilities.
Some bots specifically target older WordPress versions.
How Hiding Helps
Concealing version details adds a small but useful layer of security.
While it is not a complete defense, reducing exposed information makes automated targeting harder.
Monitor File Changes
File monitoring tools help detect suspicious activity early.
Unexpected changes may indicate:
- Malware injections
- Accès non autorisé
- Plugin vulnerabilities
- Server compromise
Common Warning Signs
Watch for:
- Modified core files
- Strange scripts
- New unknown files
- Hidden directories
- Unexpected redirects
Early detection can prevent larger security incidents.
Disable Directory Browsing
If directory browsing is enabled, visitors may view your file structure directly in the browser.
This can expose:
- Plugin folders
- Upload directories
- Sensitive files
- Backup files
Why Directory Browsing Is Dangerous
Attackers can use exposed directories to:
- Identify vulnerable plugins
- Find backup archives
- Discover hidden files
Disabling directory browsing helps reduce unnecessary exposure.
Protect Against Malware
Malware can damage your website reputation and SEO rankings.
Some malware redirects users to spam pages, while others steal sensitive information silently.
Common Malware Sources
Malware often enters through:
- Outdated plugins
- Pirated themes
- Weak passwords
- Insecure hosting
- Vulnerable file permissions
Regular scans and proactive monitoring help reduce these risks.
Avoid Nulled Themes and Plugins
Nulled software refers to pirated premium themes or plugins distributed illegally.
While they may seem free, they often contain:
- Backdoors
- Hidden malware
- Spam injections
- Tracking scripts
Why Nulled Software Is Risky
Many hacked WordPress websites trace back to infected premium downloads from untrusted sources.
Always download themes and plugins from:
- Official marketplaces
- Trusted developers
- Verified vendors
Free pirated software can end up costing far more in security damage.
Secure Your Database
Although database security is separate from file protection, the two are closely connected.
Attackers who access WordPress files may also target the database.
Helpful Database Security Practices
Good practices include:
- Strong database passwords
- Unique table prefixes
- Limited database user permissions
- Regular backups
Database security strengthens your overall WordPress protection strategy.
Utilisez un pare-feu d'application Web
A web application firewall filters malicious traffic before it reaches your website.
This helps block:
- Bots
- SQL injections
- Brute-force attacks
- Suspicious requests
Benefits of Firewalls
Firewalls can:
- Reduce server load
- Prevent automated attacks
- Improve website stability
- Block harmful IP addresses
Many security services offer cloud-based firewall protection for WordPress websites.
Regularly Scan Your Website
Routine scans help identify vulnerabilities before attackers exploit them.
Scans can detect:
- Logiciel malveillant
- Suspicious files
- Vulnerable plugins
- Blacklisting issues
- SEO spam injections
Why Regular Scanning Matters
Some infections remain hidden for weeks or months.
Frequent security checks improve your chances of catching problems early.
Educate Website Users
Security is not only a technical issue.
Anyone with website access should follow good security practices.
Important User Security Habits
Encourage users to:
- Use strong passwords
- Avoid suspicious links
- Update software regularly
- Limit unnecessary admin access
- Enable two-factor authentication
Human mistakes often create security vulnerabilities.
Réflexions finales
Understanding how to protect WordPress files is essential for maintaining a safe and reliable website. From securing sensitive files and using proper permissions to installing security plugins and monitoring file changes, every security layer helps reduce potential risks.
No single method guarantees complete protection, but combining multiple security practices creates a much stronger defense against hackers, malware, and automated attacks.
WordPress security should never be treated as a one-time task. Regular updates, backups, monitoring, and proactive maintenance all play important roles in keeping your website protected over time.
By following these best practices, website owners can improve stability, reduce vulnerabilities, and build a safer online experience for visitors and customers alike.
FAQ
1. Why is protecting WordPress files important?
Protecting WordPress files helps prevent hackers from accessing sensitive website data, injecting malware, stealing customer information, or damaging your website. Strong file security improves overall website stability and reduces vulnerabilities.
2. What are the safest file permissions for WordPress?
Most WordPress websites use:
- Dossiers :
755 - Fichiers :
644 - wp-config.php:
600ou640
These permission settings help limit unauthorized access while allowing WordPress to function properly.
3. How can I protect my wp-config.php file?
You can protect the wp-config.php file by:
- Restricting file permissions
- Blocking public access
- Moving the file outside the public directory
- Using server rules to deny external requests
This file contains important database and security information, so protecting it is critical.
4. Does hiding the WordPress version improve security?
Yes. Hiding your WordPress version makes it harder for attackers to identify known vulnerabilities associated with outdated versions. While it is not a complete security solution, it adds an extra layer of protection.
5. What is two-factor authentication in WordPress?
Two-factor authentication adds a second verification step during login, such as a mobile authentication code. Even if someone steals your password, they cannot access your account without the additional verification method.
6. Can security plugins help protect WordPress files?
Yes. WordPress security plugins can monitor file changes, scan for malware, block suspicious activity, limit login attempts, and strengthen overall website security. They are one of the easiest ways to improve WordPress protection for beginners.